Healthcare and pharmaceutical distribution giant McKesson has disclosed a significant cybersecurity incident. The company confirmed unauthorized access to third-party applications and data exfiltration. Consequently, the ShinyHunters extortion group claims it stole 284 million patient-related data records.
McKesson discovered the breach on August 25, 2026. The company says its investigation remains in the early stages. However, the scope of stolen data already appears vast.
What Happened: ShinyHunters Breaches McKesson in Massive Healthcare Data Theft
McKesson Corporation is one of the largest healthcare companies in the United States. It provides medicines, medical supplies, technology, and services to pharmacies, hospitals, clinics, and physicians nationwide. The company disclosed the incident in a Form 8-K filing with the U.S. Securities and Exchange Commission.
McKesson said it immediately activated incident response protocols upon discovery. It also engaged leading cybersecurity experts to assist with the investigation. In a customer notice, the company confirmed the incident involved third-party applications and unauthorized access and exfiltration of data.
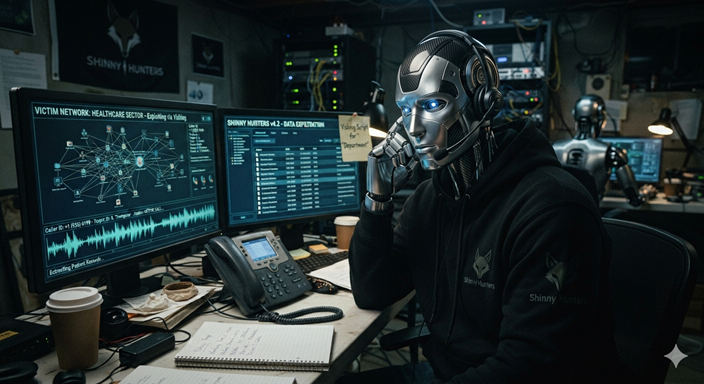
The ShinyHunters extortion group told BleepingComputer it was behind the attack. The group claims it conducted voice phishing, or vishing, social engineering attacks against multiple McKesson employees. Furthermore, it used fake .claims domains to impersonate help desks and IT teams. ReliaQuest documented this widespread ShinyHunters campaign in a recent threat research post.
According to ShinyHunters, the vishing attacks led to the compromise of multiple employees’ Okta single sign-on accounts. The threat actors then used these credentials to access McKesson’s Salesforce and Snowflake environments. ShinyHunters claims it fully compromised the Salesforce environment. It also allegedly exfiltrated about 1TB of data from Snowflake over four days between August 21 and August 25.
The stolen data allegedly contains approximately 284 million data records of patient-related information. However, ShinyHunters clarified that this figure represents raw data records, not necessarily 284 million unique individuals. The threat actor has not fully analyzed the stolen data and does not know how many unique people are affected.
ShinyHunters demanded a $55,236,150 ransom and gave McKesson 72 hours to respond. The group says McKesson did not respond to or negotiate over the ransom demand.
Technical Details of the Attack and Data Exfiltration
The attack began with vishing, a form of social engineering conducted over phone calls. ShinyHunters registered domains following a company[.]claims pattern. These domains incorporate the targeted organization’s name or abbreviation under the .claims top-level domain. For McKesson, the threat actors allegedly used mckesson[.]claims to impersonate the company’s help desk.
Once employees fell for the vishing scheme, the attackers compromised their Okta accounts. Therefore, they gained access to cloud-based SaaS platforms including Salesforce and Snowflake. This type of attack exploits trust in IT support channels rather than technical vulnerabilities in software.
ShinyHunters claims it exfiltrated the following types of data:
- Identity and contact information including full names, home addresses, dates of birth, phone numbers, email addresses, and Social Security numbers
- Healthcare identifiers such as patient IDs, medical record numbers, and Medicaid numbers
- Medical information including illnesses, diagnoses, allergies, medications, disabilities, patient notes, appointment details, and physician information
- Highly sensitive records such as hospice and terminal illness information, causes of death, and autopsy details
- Predictive health data including disease-risk assessments linked to individual patients
- Prescription and billing records with medication orders, invoices, shipment addresses, dates, and tracking numbers
- Employee records with names, addresses, email addresses, phone numbers, departments, and job roles
- Physician and clinic data including names, contact details, and practice locations
- Internal communications and doctor-patient email content
This attack comes amid an ongoing wave of data-theft campaigns targeting healthcare organizations. Health-ISAC recently warned healthcare organizations about increasing ShinyHunters attacks involving social engineering designed to compromise corporate accounts and gain access to cloud and SaaS platforms.
Business and Operational Impact
The McKesson breach carries severe implications for the healthcare sector. The potential impact includes:
- Patient privacy violations affecting potentially tens of millions of individuals
- Identity theft risks from exposed Social Security numbers, addresses, and dates of birth
- Medical identity fraud from stolen healthcare identifiers and insurance information
- Regulatory scrutiny from HIPAA and state privacy regulators
- Reputational damage to McKesson and downstream healthcare providers
- Service disruptions as McKesson implements containment measures
- Ransom demands and potential public data leaks by ShinyHunters
Healthcare technology companies recently targeted in ShinyHunters data-theft attacks include Medtronic, DentaQuest, iRhythm, OneMedical, and AdaptHealth. Therefore, this incident fits a clear pattern of healthcare-focused extortion.
Mitigation and Recommendations
Organizations connected to McKesson should take immediate steps to protect themselves. Moreover, all healthcare and enterprise organizations should review their defenses against similar vishing and SaaS account takeover attacks.
Immediate Actions for Defenders
- Audit Okta and other identity provider logs for suspicious authentication activity
- Review Salesforce and Snowflake access logs for unusual data export patterns
- Enable multi-factor authentication on all SaaS platforms, especially Okta
- Train employees to verify help desk communications through independent channels
- Block the mckesson[.]claims domain and monitor for similar .claims domains targeting your organization
- Review and tighten data loss prevention policies for cloud environments
- Notify affected patients and partners promptly per breach notification requirements
Long-Term Recommendations
Healthcare organizations should strengthen their security posture against SaaS-targeted attacks. First, implement conditional access policies that restrict logins based on geography, device compliance, and risk scores. Second, deploy endpoint detection and response solutions that can identify vishing callbacks and social engineering. Third, establish a Zero Trust architecture for cloud application access.
Bottom line: The McKesson breach demonstrates that healthcare data remains a prime target for extortion groups using social engineering rather than sophisticated malware. Organizations must prioritize identity security and employee awareness alongside traditional perimeter defenses.
Incident Summary
| Incident: | McKesson data breach by ShinyHunters |
| Discovery Date: | August 25, 2026 |
| Attack Vector: | Voice phishing (vishing) via fake .claims domains |
| Compromised Systems: | Okta SSO, Salesforce, Snowflake environments |
| Data Stolen: | ~284 million patient records (raw count), ~1TB total |
| Threat Actor: | ShinyHunters extortion group |
| Ransom Demand: | $55,236,150 (unpaid as of disclosure) |
| Patch Status: | N/A — incident under investigation |
| Severity: | Critical — mass healthcare data exposure |
References
- BleepingComputer, “McKesson discloses breach after ShinyHunters claims patient data theft,” August 29, 2026, https://www.bleepingcomputer.com/news/security/mckesson-discloses-breach-after-shinyhunters-claims-patient-data-theft/.
- CyberInsider, “ShinyHunters claims McKesson data breach exposing 284 million patient records,” August 29, 2026, https://cyberinsider.com/mckesson-data-breach-exposing-284-million-patients/.
- U.S. Securities and Exchange Commission, “McKesson Corporation Form 8-K,” August 25, 2026, https://www.sec.gov/Archives/edgar/data/927653/000092765326000247/mck-20260825.htm.
- McKesson Corporation, “Customer Cybersecurity Information Center,” accessed August 30, 2026, https://www.mckesson.com/utility/cybersecurity/customer-cybersecurity-information-center/.
- ReliaQuest Threat Research, “ShinyHunters .claims domain campaign,” August 2026, https://x.com/ReliaQuestTR/status/2089393351078354988.
- BleepingComputer, “Health-ISAC warns of rising ShinyHunters data-theft attacks on healthcare,” August 2026, https://www.bleepingcomputer.com/news/security/health-isac-warns-of-rising-shinyhunters-data-theft-attacks-on-healthcare/.