CISA Adds Cisco BroadWorks XXE CVE to KEV Catalog
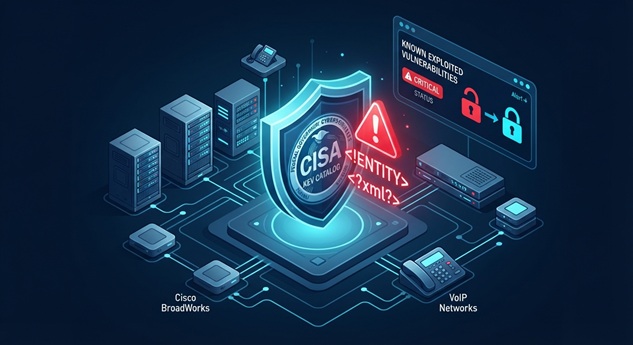
CISA added CVE-2026-20320 to its Known Exploited Vulnerabilities Catalog on November 10, 2026. This high-severity flaw in Cisco BroadWorks lets unauthenticated remote attackers read sensitive configuration data via a crafted XML message. Threat actors are already exploiting it in the wild, including in autonomous AI-driven intrusions.
What Happened: Cisco BroadWorks XXE Flaw Added to CISA KEV
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) warned that hackers are actively exploiting CVE-2026-20320. Cisco patched this vulnerability in August 2026, but attackers continue to target unpatched systems.
The vulnerability resides in the Open Client Interface (OCI) XML parser within Cisco BroadWorks. It allows unauthenticated remote attackers to read sensitive files by sending malicious XML messages. CISA added the flaw to its KEV catalog on November 10 and gave federal agencies until November 24 to patch.
Threat intelligence firm Malbear Labs reported that a Chinese-speaking actor exploited CVE-2026-20320 using a jailbroken DeepSeek Flash AI model. The campaign targeted a European telecom provider and thirteen downstream organizations.
Technical Details of the Cisco BroadWorks Vulnerability
CVE-2026-20320 is an XML External Entity (XXE) injection vulnerability. The BroadWorks OCI XML parser processes external entity references by default. This allows an attacker to include external resources in XML documents.
An attacker sends a crafted XML message to the OCI-P service on port 2208. The parser resolves external entities and returns file contents from the server filesystem. No authentication is required to exploit this flaw.
- CVE ID: CVE-2026-20320
- CVSS Score: High severity (exact score pending NVD update)
- Attack Vector: Network
- Privileges Required: None
- User Interaction: None
- Affected Component: Cisco BroadWorks OCI XML Parser
- Service Port: 2208/TCP (OCI-P)
In the observed attacks, the threat actor used an autonomous AI agent to craft and send XXE payloads. The agent recovered system identity private keys, SSL credentials, and additional private keys from the XSP host. These credentials enable impersonation of BroadWorks components in inter-component communication.
Business and Operational Impact
Successful exploitation grants attackers access to sensitive BroadWorks configuration data. This can lead to broader compromise of telecom infrastructure.
- Telecom provider exposure: Service provider and MSP platforms at risk
- Subscriber data: Configuration files may contain subscriber records
- Credential theft: Private keys and SSL certificates enable lateral movement
- Service disruption: Compromised systems may experience outages
- Supply chain risk: Downstream customers of affected providers are also exposed
Malbear Labs confirmed that thirteen organizations using a compromised telecom provider’s infrastructure were targeted. This demonstrates the cascading impact of a single vulnerable system.
Mitigation and Recommendations
Organizations running Cisco BroadWorks should act immediately. CISA has set a federal patching deadline of November 24, 2026. Private sector organizations should follow the same timeline.
Immediate Actions for Defenders
- Apply the Cisco BroadWorks patch released in August 2026 without delay.
- Restrict network access to OCI-P service port 2208 from untrusted sources.
- Review BroadWorks logs for suspicious XML payloads to port 2208.
- Rotate all SSL certificates and private keys stored on BroadWorks systems.
- Audit inter-component authentication to detect potential impersonation.
Detection and Monitoring Guidance
Security teams should monitor for indicators of compromise related to CVE-2026-20320. Look for unexpected file access on BroadWorks servers and anomalous XML traffic to the OCI-P service.
Bottom line: CVE-2026-20320 is a high-severity, unauthenticated XXE flaw being actively exploited. Patch immediately, restrict network access, and rotate credentials to protect your BroadWorks infrastructure.
Incident Summary
| CVE ID / Incident: | CVE-2026-20320 |
| Affected Systems: | Cisco BroadWorks (OCI XML Parser) |
| Disclosure Date: | August 2026 (patched); November 10, 2026 (CISA KEV addition) |
| Patch Status: | Patch available; federal deadline November 24, 2026 |
References
- Sergiu Gatlan, “CISA flags Cisco BroadWorks flaw as actively exploited in attacks,” BleepingComputer, November 11, 2026. https://www.bleepingcomputer.com/news/security/cisa-flags-cisco-broadworks-flaw-as-actively-exploited-in-attacks/
- CISA, “CISA Adds Six Known Exploited Vulnerabilities to Catalog,” November 10, 2026. https://www.cisa.gov/news-events/alerts/2026/11/10/cisa-adds-six-known-exploited-vulnerabilities-catalog
- Cisco Security Advisory, “Cisco BroadWorks Open Client Interface XML Parser XML External Entity Injection Vulnerability,” August 2026. https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-bworks-xxe-uwUd7CEt
- Malbear Labs, “Operation Snowball: Inside an Autonomous AI Intrusion Campaign,” November 2026. https://malbearlabs.com/posts/operation-snowball-inside-an-autonomous-ai-intrusion-campaign
- NVD, “CVE-2026-20320 Detail,” National Vulnerability Database. https://nvd.nist.gov/vuln/detail/CVE-2026-20320