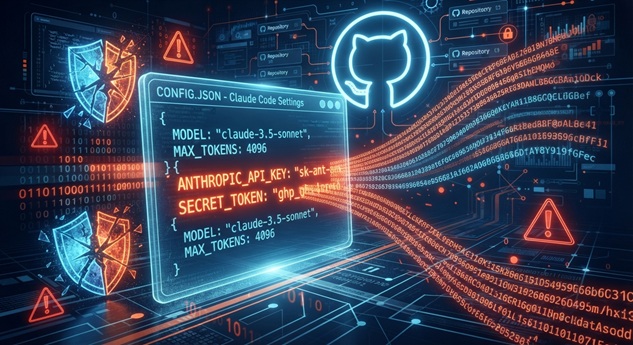
Developers using Anthropic’s Claude Code are accidentally leaking passwords and API keys into public GitHub repositories. The AI coding assistant can save approved commands containing plaintext secrets in a project settings file. Researchers at Apiiro found 1,122 public copies of the file with at least one live secret.
What Happened: Claude Code Settings File Leaks Secrets on GitHub
Claude Code is an AI-powered coding assistant from Anthropic. It asks users before running most shell commands. When a user selects “Yes, and don’t ask again,” the tool saves an allow rule in .claude/settings.local.json inside the project directory.
However, when the approved command is an exact command (not a pattern) and the user typed a password or token into it, that secret is saved word-for-word in plain text. Consequently, developers who commit this file to GitHub expose credentials to anyone who can read the repository.
Apiiro discovered 104,185 copies of the file across 103,617 public repositories. About 1.1% of them, or 1,122 copies, hold at least one secret. Together they contain 1,379 different secrets.
Technical Details of the Vulnerability
The issue stems from how Claude Code stores command approval rules. By default, it adds the file to the user’s global git excludes on the first write. Therefore, the file is ignored locally. However, this protection does not travel with the project.
Claude Code never adds the file to the project’s own .gitignore. If the file was already committed before the global exclude was set, it remains in git history. Furthermore, older versions stay in history even after deletion, and forks of the repository spread the secrets further.
Apiiro traced 539 of 1,105 repositories where a commit listing Claude as a co-author changed the file. This suggests Claude itself may commit the file during automated operations.
What Secrets Are Leaked
- 379 database passwords
- 43 SSH logins for public servers
- 42 tokens for GitHub, GitLab, and npm
- 23 AWS keys
- Additional tokens, API keys, and credentials across 63 organizations
Scope and Impact
Moreover, the researchers found 734 additional secrets across 509 repositories in older versions of the file that are no longer present in current copies. Including the shared .claude/settings.json file and saved agent chat logs, the total reaches 2,539 secrets across 1,994 repositories.
Of 16 coding agents whose documentation Apiiro compared, Claude Code is the only one confirmed to save the full approved command in a project file by default.
Business and Operational Impact
This leak affects organizations of all sizes, including software companies and database vendors. In one case, a database vendor’s admin-level cloud key was exposed. In another, the owner password of a medical-records database was leaked.
- Compromised credentials can lead to unauthorized data access
- Attackers may gain lateral movement into connected infrastructure
- Deployment secrets and application keys are at risk
- Git history and forks make cleanup difficult
- Secret scanners miss many of these leaks
Also, common tools like gitleaks flagged only 564 of the 1,122 files with secrets. TruffleHog flagged 643. Neither caught 215 files. Most misses are passwords typed inside commands, which scanners treat as ordinary words rather than secrets.
Mitigation and Recommendations
Immediate Actions for Developers
- Search your GitHub organization for
.claude/settings.local.jsonand.claude/settings.json - Check each repository’s git history, even where the files are gone
- Rotate every password, token, and key the files have ever held
- Stop tracking the local file with
git rm --cached .claude/settings.local.json - Add the file to your repository’s own
.gitignore - Delete every rule containing a secret from the file on your local machine
Secure Development Practices
Keep secrets out of commands. Refer to them as variables from a secrets manager, such as $DB_URL, so the saved rule holds the variable name and not the secret. Approve patterns like Bash(npm run:*) instead of single commands.
For Security Teams
- Treat agent folders like
.claude/,.cursor/,.gemini/, and agent memory files as secret-bearing - Add them to pre-commit and CI secret scanning, including git history
- Ensure scanners catch passwords inside commands, not only known key formats
- Add
.claude/settings.local.jsonto organizational.gitignoretemplates - Prioritize credentials paired with public servers first
Bottom line: Rotate every secret that has ever passed through Claude Code. Then clean up the files. The leak is already public, and attackers know where to look.
Incident Summary
| Incident: | Claude Code “Don’t Ask Again” File Leaks Secrets on GitHub |
| Affected Product: | Anthropic Claude Code AI coding assistant |
| Disclosure Date: | November 6, 2026 |
| Researcher: | Apiiro |
| Secrets Found: | 1,379 distinct secrets in 1,122 public files |
| Total Exposed: | 2,539 secrets across 1,994 repositories |
| Patch Status: | No patch available; mitigation requires developer action and secret rotation |
References
- Apiiro, “Coding Agents Are Leaking Secrets on GitHub: The ‘Don’t Ask Again’ Problem,” November 6, 2026, https://apiiro.com/blog/coding-agents-leaking-secrets-github-dont-ask-again, accessed November 7, 2026.
- The Hacker News, “Claude Code’s ‘Don’t Ask Again’ File Exposes Passwords and Keys in 1,122 Public Copies on GitHub,” November 7, 2026, https://thehackernews.com/2026/11/claude-codes-dont-ask-again-file.html, accessed November 7, 2026.
- Anthropic, “Permissions — Claude Code Documentation,” https://code.claude.com/docs/en/permissions, accessed November 7, 2026.
- Anthropic, “Settings — Claude Code Documentation,” https://code.claude.com/docs/en/settings, accessed November 7, 2026.
- GitHub Issue #5544, “Claude Code saves API keys in settings.local.json,” August 11, 2025, https://github.com/anthropics/claude-code/issues/5544, accessed November 7, 2026.