SonicWall SSL-VPN MFA Bypass CVE, CISA Confirms Active Exploitation
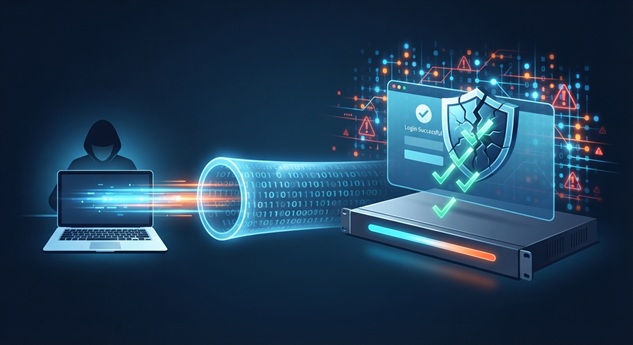
SonicWall has patched a critical SSL-VPN authentication bypass vulnerability that allows attackers to circumvent multi-factor authentication controls on affected firewalls. The flaw, tracked as CVE-2026-19868, carries a CVSS score of 7.1 and has been actively exploited in the wild, prompting CISA to add it to the Known Exploited Vulnerabilities catalog.
What Happened: SonicWall SSL-VPN MFA Bypass Enables Authentication Circumvention
SonicWall disclosed seven vulnerabilities in SonicOS firewalls on November 6, 2026. The most severe of these, CVE-2026-19868, allows attackers with valid credentials for an alternate authentication method to bypass SAML authentication controls. Consequently, attackers can potentially bypass SAML-enforced multi-factor authentication.
The vulnerability only affects SonicOS SSL-VPN services configured to use SAML authentication. SonicWall confirmed it had investigated a report indicating potential exploitation of this flaw. Furthermore, CISA added CVE-2026-19868 to its Known Exploited Vulnerabilities catalog, confirming active exploitation.
Ryan Harris of The Electronic Office discovered and reported this vulnerability. CISA has ordered federal civilian executive branch agencies to secure affected systems by November 20, 2026.
Technical Details of the SonicWall SSL-VPN Authentication Bypass
CVE-2026-19868 stems from improper validation during the SAML authentication process in SonicOS SSL-VPN services. Attackers can exploit the flaw by authenticating through an alternate method while SAML MFA enforcement is active.
The November 2026 advisory also addresses six additional SonicOS vulnerabilities:
- Two management interface flaws (CVSS 8.8): Allow unauthenticated attackers to perform unauthorized operations under specific conditions
- Pre-authentication buffer overflows in SSL-VPN and TACACS+ services: Could cause denial-of-service conditions
- Weak password hashing vulnerability: Affects virtual appliances
The vulnerabilities affect SonicOS Gen7 versions 7.3.3-7015 and earlier, and Gen8 versions 8.2.2-8015 and earlier. SonicWall fixed the issues in versions 7.3.4-7013 and 8.2.3-8015.
Business and Operational Impact
Organizations using affected SonicWall firewalls face significant security risks. Successful exploitation can have severe consequences:
- Authentication bypass: Attackers can gain VPN access without proper MFA verification
- Lateral movement: Compromised VPN access enables attackers to pivot within corporate networks
- Data exposure: Sensitive internal resources become accessible to unauthorized actors
- Compliance violations: MFA bypass incidents may trigger regulatory reporting requirements
This disclosure follows a troubling pattern of attacks targeting SonicWall remote access infrastructure. In October 2026, researchers detected exploitation attempts against CVE-2026-102255, a maximum-severity SMA1000 vulnerability. Moreover, September 2026 saw attackers chain two SMA1000 zero-days for remote code execution.
Mitigation and Recommendations
SonicWall has released patched firmware versions and strongly urges immediate upgrades. No workarounds are available for CVE-2026-19868.
Immediate Actions for Defenders
- Upgrade SonicOS Gen7 to version 7.3.4-7013 or later
- Upgrade SonicOS Gen8 to version 8.2.3-8015 or later
- Review VPN access logs for unusual authentication patterns
- Audit SAML configuration settings across all SSL-VPN deployments
- Monitor for indicators of compromise from affected timeframes
Long-Term Security Measures
Organizations should also consider broader network security improvements. First, implement network segmentation to limit VPN user access to essential resources only. Second, deploy additional MFA layers beyond SAML where possible. Third, establish a routine patch management cycle for edge security devices.
Bottom line: SonicWall SSL-VPN users must patch immediately. With confirmed active exploitation and a CISA patching deadline of November 20, 2026, delay is not an option.
Incident Summary
| CVE ID / Incident: | CVE-2026-19868 |
| Affected Systems: | SonicOS Gen7 ≤7.3.3-7015, Gen8 ≤8.2.2-8015 with SAML SSL-VPN |
| Disclosure Date: | November 6, 2026 |
| Patch Status: | Available — SonicOS 7.3.4-7013 and 8.2.3-8015 |
| CVSS Score: | 7.1 |
| CISA KEV: | Added November 2026; federal patch deadline November 20, 2026 |
| Discovered By: | Ryan Harris, The Electronic Office |
References
- Lawrence Abrams, “SonicWall warns of new SSL-VPN MFA bypass flaw exploited in attacks,” BleepingComputer, November 6, 2026, https://www.bleepingcomputer.com/news/security/sonicwall-warns-of-new-ssl-vpn-mfa-bypass-flaw-exploited-in-attacks/, accessed November 7, 2026.
- SonicWall PSIRT, “SonicOS SSL-VPN SAML Authentication Bypass,” Security Advisory SNWLID-2026-0014, November 2026, https://psirt.global.sonicwall.com/vuln-detail/SNWLID-2026-0014, accessed November 7, 2026.
- U.S. Cybersecurity and Infrastructure Security Agency (CISA), “Known Exploited Vulnerabilities Catalog,” https://www.cisa.gov/known-exploited-vulnerabilities-catalog, accessed November 7, 2026.
- BleepingComputer, “Max severity SonicWall SMA1000 flaw now exploited in attacks,” October 2026, https://www.bleepingcomputer.com/news/security/max-severity-sonicwall-sma1000-flaw-now-exploited-in-attacks/, accessed November 7, 2026.