Drupal Commerce Core Active Access Bypass Threatens 42,000 E-Commerce Sites
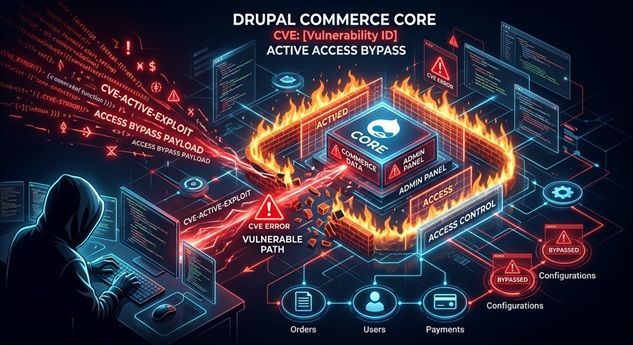
Drupal warned administrators this week that attackers are actively exploiting a critical access bypass vulnerability in the Commerce Core module. Tracked as CVE-2026-118539, the flaw allows unauthenticated threat actors to bypass authorization checks on e-commerce sites, potentially manipulating orders and causing direct financial harm to vendors. With over 42,000 websites using Commerce Core — including Fortune 500 companies and research universities — the impact is substantial.
What Happened: Drupal Commerce Core Under Active Attack
On October 29, 2026, the Drupal Security Team issued a highly critical advisory for CVE-2026-118539. The vulnerability stems from missing authorization checks in the Commerce Core module. Consequently, certain routes and entity fields remain unprotected, enabling forceful browsing by unauthenticated attackers.
The Commerce Core module powers shopping carts, checkout forms, and API-driven decoupled applications for Drupal-based online stores. Because the flaw is being actively exploited in the wild, Drupal urged admins to patch immediately and audit orders for inconsistencies.
Researchers Dan Puccetti, Marcus Johansson, and Robert Snyder reported the vulnerability. Drupal confirmed active exploitation and released patched versions for affected branches.
Technical Details of the CVE-2026-118539 Vulnerability
CVE-2026-118539 is classified as a missing authorization vulnerability. It allows unauthenticated attackers to access restricted routes and entity fields within Commerce Core.
- Attack vector: Network — remote, unauthenticated
- Root cause: Insufficient authorization checks on Commerce Core routes and fields
- Impact: Forceful browsing, potential order manipulation, financial loss
- Affected versions: Commerce Core 0.0.0 through 2.41 and 3.0.0 through 3.3.13
Unlike remote code execution flaws, this access bypass does not require complex exploit chains. An attacker simply needs to reach an unprotected endpoint to interact with e-commerce data in ways the module never intended.
Business and Operational Impact
The risk here is direct revenue loss and operational disruption. Drupal explicitly warned that the access bypass “may financially impact the vendor.” Real-world consequences include:
- Order manipulation: Attackers may create, modify, or cancel orders
- Revenue loss: Unauthorized discounts or refunds can hit the bottom line
- Customer trust erosion: Visible order inconsistencies damage brand reputation
- Compliance exposure: E-commerce breaches may trigger PCI-DSS and GDPR obligations
Furthermore, the advisory specifically asks administrators to audit orders for inconsistencies. This signals that exploitation is not theoretical — it is happening now.
Mitigation and Recommendations
Drupal released patched versions quickly. Therefore, the most effective mitigation is immediate patching.
Immediate Actions for Defenders
- Upgrade Commerce Core immediately. Move to version 3.3.13 (3.x branch) or 8.x-2.41 (earlier versions).
- Audit orders for inconsistencies. Review recent transactions for unauthorized changes or anomalies.
- Review access logs. Look for unusual GET or POST requests targeting Commerce Core endpoints.
- Restrict access where possible. Use Web Application Firewall rules to block suspicious traffic to e-commerce endpoints.
- Monitor for repeat incidents. Subscribe to Drupal security advisories for follow-up alerts.
Additional Hardening Measures
Moreover, consider these broader Drupal security practices:
- Enable two-factor authentication for admin accounts
- Restrict administrative access by IP address
- Apply security patches within 24 hours of release for internet-facing sites
- Maintain offline backups of order databases
Bottom line: If you run a Drupal Commerce site, patch today and audit your orders. Active exploitation means every hour of delay increases the chance of financial loss.
Incident Summary
| CVE ID / Incident: | CVE-2026-118539 |
| Affected Systems: | Drupal Commerce Core versions 0.0.0–2.41 and 3.0.0–3.3.13 |
| Disclosure Date: | October 29, 2026 |
| Patch Status: | Fixed in Commerce Core 3.3.13 and 8.x-2.41 |
| Severity: | Highly Critical — active exploitation confirmed |
| Reporter(s): | Dan Puccetti, Marcus Johansson, Robert Snyder |
References
- Drupal Security Advisory SA-CONTRIB-2026-254, “Highly Critical — Commerce Core — Access Bypass,” October 29, 2026, https://www.drupal.org/sa-contrib-2026-254, accessed November 3, 2026.
- BleepingComputer, “Drupal warns of critical Commerce Core flaw exploited in attacks,” October 2026, https://www.bleepingcomputer.com/news/security/drupal-warns-of-critical-commerce-core-flaw-exploited-in-attacks/, accessed November 3, 2026.
- Security Affairs, “Attackers Exploit Critical Drupal Commerce Core Vulnerability CVE-2026-118539,” November 2026, https://securityaffairs.com/202162/security/attackers-exploit-critical-drupal-commerce-core-vulnerability-cve-2026-118539.html, accessed November 3, 2026.