November 2, 2026
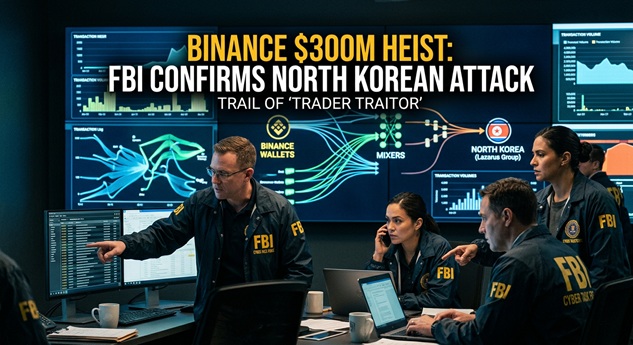
The FBI has officially attributed a record-breaking $6.3 billion cryptocurrency heist at Binance to North Korean state-sponsored hackers. The attack, which unfolded on October 29, 2026, stands as the largest crypto theft in history. Moreover, it exposes the devastating consequences of targeted social engineering against high-value financial infrastructure.
What Happened: TraderTraitor Group Drains $6.3 Billion from Binance in Minutes
On October 29, 2026, attackers stole approximately $6.36 billion in digital assets from Binance. The theft spanned ten blockchains, with most funds transferred in roughly 20 minutes. Consequently, Binance immediately suspended withdrawals to prevent further losses.
The FBI identified the threat actor as TraderTraitor. This North Korean group is also known as Lazarus Group, Jade Sleet, and APT38. Furthermore, blockchain intelligence firms TRM Labs and Chainalysis had already linked the breach to TraderTraitor before the FBI’s official confirmation.
Binance traced the initial access to a compromised DevOps engineer’s laptop. The attackers leveraged this access to reach a service container and submit unauthorized withdrawal transactions. Therefore, the breach did not exploit a software vulnerability but rather exploited human trust and endpoint security gaps.
Technical Details of the Binance Heist
The attack relied on compromising a privileged employee endpoint rather than exploiting a platform-level vulnerability. However, the scale and speed of the theft reveal a highly capable adversary with deep operational planning.
Attack Chain Summary
- Initial Access: Compromised DevOps engineer laptop
- Lateral Movement: Access to a service container with withdrawal privileges
- Execution: Unauthorized withdrawal transactions across ten blockchains
- Exfiltration: Approximately $6.36 billion moved in ~20 minutes
- Laundering: Assets converted primarily to Ethereum for DeFi mixing
The FBI has observed TraderTraitor converting stolen assets primarily into Ethereum. The agency expects further laundering through decentralized finance platforms and instant cryptocurrency swap services. Additionally, the FBI published a list of 628 cryptocurrency addresses tied to the theft. This list includes 608 Ethereum addresses, 19 Bitcoin addresses, and one Solana address.
TraderTraitor’s Known Tactics
North Korean Lazarus hackers have operated the long-running Operation DreamJob campaign. In this operation, they impersonate recruiters and approach software developers and cryptocurrency employees with fake job offers. Consequently, victims install malware disguised as pre-employment tests or code samples.
Previous attacks followed a similar pattern. The $1.5 billion Bybit heist in February 2025 stemmed from a compromised Safe{Wallet} developer computer. The $308 million DMM Bitcoin theft in May 2024 involved a recruiter impersonation on LinkedIn that tricked an employee into running malicious Python code. Furthermore, the April 2026 Drift attack involved a six-month in-person social engineering operation at industry conferences.
Business and Operational Impact
The Binance heist carries far-reaching consequences for the cryptocurrency industry, global finance, and enterprise security practices. Key impacts include:
- Largest Crypto Theft on Record: At $6.3 billion, this heist dwarfs the previous $1.5 billion Bybit record.
- Exchange Trust Erosion: Customers face uncertainty about withdrawal access and fund backing.
- Regulatory Scrutiny: Governments worldwide will likely tighten exchange oversight and compliance requirements.
- Employee Targeting Trend: The attack reinforces that privileged insiders and developers are the primary attack vector.
- DeFi Laundering Risk: Decentralized platforms face pressure to block known hacker addresses.
- National Security Dimension: State-sponsored theft directly funds the North Korean regime.
Binance has stated it will bear the financial impact and will not pass losses to users. The exchange has covered approximately 95% of the stolen amount. The remaining 5% consists of less-liquid tokens that Binance is acquiring through market and over-the-counter channels.
Mitigation and Recommendations
Organizations holding digital assets must treat this incident as a wake-up call. Therefore, immediate and long-term actions are essential to reduce exposure to similar attacks.
Immediate Actions for Cryptocurrency Exchanges
- Block Known Addresses: Update wallet monitoring and transaction blocking rules for the 628 published addresses.
- Harden DevOps Endpoints: Isolate developer and operations machines from general corporate networks. Enforce application whitelisting and EDR.
- Enhance Withdrawal Controls: Implement multi-party approval for large withdrawals. Require hardware-security-module signed transactions.
- Audit Container Access: Review service container permissions and enforce least-privilege access.
- Monitor for Social Engineering: Train employees on Operation DreamJob tactics. Verify recruiter identities independently.
Actions for Enterprise Security Teams
- Endpoint Segmentation: Separate privileged engineering workstations from internet access and email.
- Enhanced Email Filtering: Flag external communications claiming to be recruiters, especially those with attachments or links.
- Incident Response Drills: Run tabletop exercises simulating rapid exfiltration of high-value assets.
- Threat Intelligence Sharing: Participate in industry groups tracking North Korean actor infrastructure and wallet addresses.
Bottom line: The Binance heist proves that the most valuable targets in cryptocurrency are not smart contracts but the people who operate them. Hardening human endpoints is now the highest-return security investment.
Incident Summary
| Incident ID: | Binance $6.3B Crypto Heist (October 29, 2026) |
| Threat Actor: | TraderTraitor (Lazarus Group / Jade Sleet / APT38) |
| Affected Organization: | Binance Cryptocurrency Exchange |
| Disclosure Date: | October 29, 2026 (FBI attribution: November 1, 2026) |
| Attack Vector: | Compromised DevOps engineer laptop |
| Financial Impact: | ~$6.36 billion stolen across ten blockchains |
| Recovery Status: | ~95% of losses covered by Binance; withdrawals resumed |
References
- FBI Cyber Division, “North Korea Responsible for $6 Billion Binance Attack,” November 1, 2026, http://www.fbi.gov/investigate/cyber/alerts/2026/north-korea-responsible-for-6-billion-binance-attack, accessed November 2, 2026.
- BleepingComputer, Lawrence Abrams, “FBI links $6.3 billion Binance crypto heist to North Korean hackers,” November 1, 2026, https://www.bleepingcomputer.com/news/security/fbi-links-63-billion-binance-crypto-heist-to-north-korean-hackers/, accessed November 2, 2026.
- The New York Times, “How Binance’s $6.3 Billion Hack Went Down,” October 31, 2026, https://www.nytimes.com/2026/10/31/technology/binance-hack-crypto-north-korea.html, accessed November 2, 2026.
- NPR, “A simple explainer of the massive $6.3 billion crypto heist at Binance,” October 31, 2026, https://www.npr.org/2026/10/31/nx-s1-6024426/binance-crypto-heist-cyber-criminals-north-korea, accessed November 2, 2026.
- Reuters, “North Korean hackers linked to crypto thefts among world’s best, experts say,” October 30, 2026, https://www.reuters.com/legal/government/north-korean-hackers-linked-crypto-thefts-among-worlds-best-experts-say-2026-10-30/, accessed November 2, 2026.