Ledger Hardware Wallet Supply Chain Attack: Seed Phrase Implant Steals Crypto via LTE
October 15, 2026
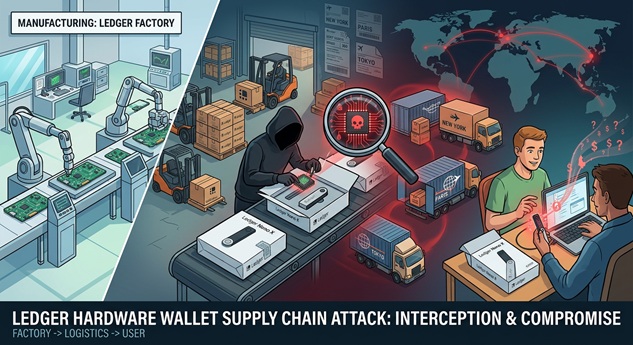
Cryptocurrency hardware wallet manufacturer Ledger has halted sales across Southeast Asia and Hong Kong after confirming that reseller devices were tampered with to steal seed phrases over LTE. The supply chain attack involves a physical hardware implant that intercepts recovery phrases and exfiltrates them remotely without altering the device firmware.
What Happened: Ledger Reseller Devices Implanted with Seed Phrase Spy Chip
On October 14, 2026, Ledger announced it was investigating reports of tampered hardware wallets sold by third-party resellers. The incident centers on devices sold by CryptoBilis, a Southeast Asian reseller, which were found to contain a malicious hardware implant.
Ledger’s Donjon security team confirmed the implant includes a microcontroller that detects and decodes the 24-word recovery phrase during wallet setup or restoration. Furthermore, the implant transmits the stolen seed phrase over LTE using a provisioned eSIM to attacker-controlled infrastructure.
The company also reported that users have observed compromised devices from additional sellers across Asia and Europe. These reports include purchases from Metapod at Singapore Changi Airport and from MediaMarkt in Europe. Consequently, Ledger ordered a sales halt covering all distributors in Indonesia, Singapore, Thailand, the Philippines, Vietnam, Malaysia, and Hong Kong until device safety investigations are complete.
Technical Details of the Hardware Implant Attack
The hardware implant represents a sophisticated supply chain compromise that bypasses traditional software security measures.
How the Implant Works
- The implant is a separate physical component added to the device during or after distribution
- It monitors the screen or bus to detect and decode the 24-word recovery phrase
- Captured seed phrases are transmitted over LTE via a provisioned eSIM
- The implant does not modify the Secure Element or Ledger operating system
- It does not alter transactions or signatures, avoiding detection by integrity checks
Why Traditional Defenses Fail
Because the implant operates independently of the wallet’s secure firmware, it evades standard verification methods. Ledger’s integrity self-checks examine the operating system and Secure Element but cannot detect added hardware components that simply observe and exfiltrate data. In addition, because the implant uses its own cellular connectivity, it does not rely on the victim’s network and can operate even when the wallet is not connected to a computer or mobile device.
Business and Operational Impact
The incident has significant consequences for both individual cryptocurrency holders and the broader hardware wallet industry.
- Direct financial losses: Multiple users reported cryptocurrency theft after setting up compromised devices
- Supply chain trust erosion: Consumers may avoid third-party resellers or hardware wallets altogether
- Reseller network disruption: Ledger halted sales across eight markets; Trezor announced plans to reduce its reseller network
- Regulatory scrutiny: Hardware wallet vendors may face increased oversight of distribution channels
- Industry-wide response: Competitor Trezor acted preemptively to tighten reseller controls despite no confirmed compromises of its devices
Mitigation and Recommendations
Immediate Actions for Hardware Wallet Users
- Purchase devices only through the manufacturer’s official direct sales channel or authorized retailers with verified supply chain controls
- Inspect the device packaging for tampering, unusual seals, or signs of opening
- Consider initializing the wallet in an isolated environment without internet connectivity
- If a device was purchased from an affected reseller, do not use it; transfer funds to a new wallet from a trusted source
- Monitor cryptocurrency accounts for unauthorized transactions if a suspicious device was used
Actions for Enterprises and Resellers
- Conduct supply chain security audits of hardware partners and distributors
- Implement tamper-evident packaging and secure logistics controls
- Require cryptographic attestation of device integrity at point of sale
- Establish incident response procedures for supply chain compromises
Bottom line: Physical hardware implants can bypass even the strongest firmware protections. Purchase hardware wallets only from trusted, direct channels and inspect devices for tampering before use.
Incident Summary
| Incident: | Ledger Hardware Wallet Supply Chain Attack |
| Affected Products: | Ledger hardware wallets sold by third-party resellers, primarily CryptoBilis |
| Attack Vector: | Physical hardware implant with LTE eSIM exfiltration |
| Disclosure Date: | October 14, 2026 |
| Impact: | Cryptocurrency theft via stolen recovery phrases |
| Status: | Sales halted in 8 markets; investigation ongoing |
References
- BleepingComputer, “Ledger asks sellers across Asia to halt sales after supply-chain attack,” October 14, 2026, https://www.bleepingcomputer.com/news/security/ledger-asks-sellers-across-asia-to-halt-sales-after-supply-chain-attack/
- Ledger Donjon (Twitter/X), hardware implant technical details, October 13, 2026, https://x.com/Ledger/status/2109896739985453358
- BleepingComputer, “Ledger confirms hardware wallet spy implant behind crypto thefts,” October 10, 2026, https://www.bleepingcomputer.com/news/security/ledger-confirms-hardware-wallet-spy-implant-behind-crypto-thefts/
- Mark Karpelès (Twitter/X), initial implant discovery report, October 2026, https://x.com/MagicalTux/status/2109916873689280900
- Trezor (Twitter/X), reseller network reduction announcement, October 2026, https://x.com/Dantoshi/status/2110000117856248141