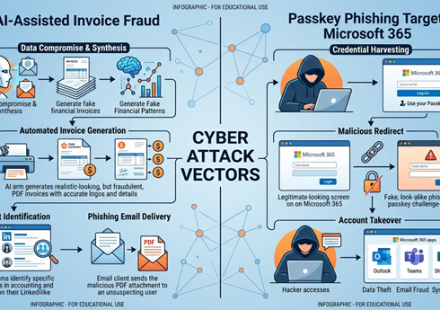
Microsoft Discloses AI-Assisted Invoice Fraud and Passkey Phishing Campaigns

Microsoft has disclosed details of two active campaigns targeting enterprise cloud environments through AI-assisted executive impersonation and passkey-themed social engineering. The attacks leverage third-party email delivery infrastructure to bypass…
UNC3569 Exploits Sogou Input Method Flaw to Deploy GRAYRABBIT Backdoor
September 13, 2026 Threat actors linked to a China-aligned espionage group are exploiting a critical vulnerability (CVE-2026-51990) in Tencent’s Sogou Input Method for Windows to deploy the GrayRabbit backdoor. The flaw allows one-click remote code…
Passkey-Themed Phishing Attacks Target Microsoft 365
September 11, 2026 Microsoft has confirmed that threat actors linked to the ShinyHunters and Helix extortion gangs are conducting sophisticated passkey-themed phishing campaigns that compromise corporate Microsoft 365 accounts and steal sensitive data.…
Critical Path Traversal Flaw Under Active Exploitation
September 11, 2026 On September 10, 2026, GitLab disclosed CVE-2026-85706, a maximum-severity path traversal vulnerability in its repository commits API. The flaw carries a CVSS score of 10.0 and allows unauthenticated attackers to read arbitrary files…
Cisco Critical FMC Authentication Bypass Confirmed Under Active Exploitation
September 10, 2026 Cisco has confirmed that a maximum-severity authentication bypass vulnerability tracked as CVE-2026-20079 in its Secure Firewall Management Center (FMC) software is being actively exploited in attacks. Furthermore, the U.S.…
ShieldCrash Zero-Day Bypasses Microsoft Defender Patch and Grants SYSTEM Access
An anonymous security researcher known as Nightmare Eclipse has released a new Microsoft Defender zero-day exploit named ShieldCrash on September 9, 2026. The exploit bypasses a recently patched Defender flaw called ShieldBreak and grants SYSTEM…
Critical Kernel Flaw Enables Unauthenticated Remote Code Execution
September 9, 2026 SAP has patched a maximum-severity vulnerability in its kernel that enables unauthenticated remote code execution with administrative privileges. Tracked as CVE-2026-44756 and codenamed OVERPASS, the flaw carries a CVSS score of 10.0…
PEEP Toolkit Turns Chrome and Edge Into Post-Compromise Backdoors
September 8, 2026 A newly disclosed post-exploitation toolkit called PEEP is turning Google Chrome and Microsoft Edge into persistent backdoors for host-level command execution. Cybersecurity researchers at SOCRadar disclosed the framework this week,…
MikroTik RouterOS Attack Chain Hijacks Devices
September 7, 2026 Threat actors are actively exploiting a chain of two critical vulnerabilities in MikroTik routers. The attack, dubbed “MikroTrick,” allows hackers to bypass SSH authentication and escalate privileges to gain full administrative control…
StyleSmuggler Magento and Adobe Commerce Zero-Day
September 06, 2026 Attackers are actively exploiting a new unpatched vulnerability in Magento Open Source and Adobe Commerce that lets them run malicious code on an online store’s server without logging in. Dutch e-commerce security company Sansec…